Personal, authorized AWS lab. This page describes a completed engineering project, not paid SOC work, a production security service, or a response to real attackers. Local dashboard demonstrations contain synthetic fixtures. The October 13, 2026 automatic rollback result comes from a separate, historical live-lab acceptance test.
At a Glance
- 6 source-reviewed CloudTrail Python heuristics covering root activity, login failures, denied API calls, CloudTrail configuration, IAM permission changes and S3 policy changes.
- 8 local read-only analyst views, including Overview, Investigations, Case Dossier, Approval Gate, Response Operations, Forensic Audit, Architecture and Settings/Posture.
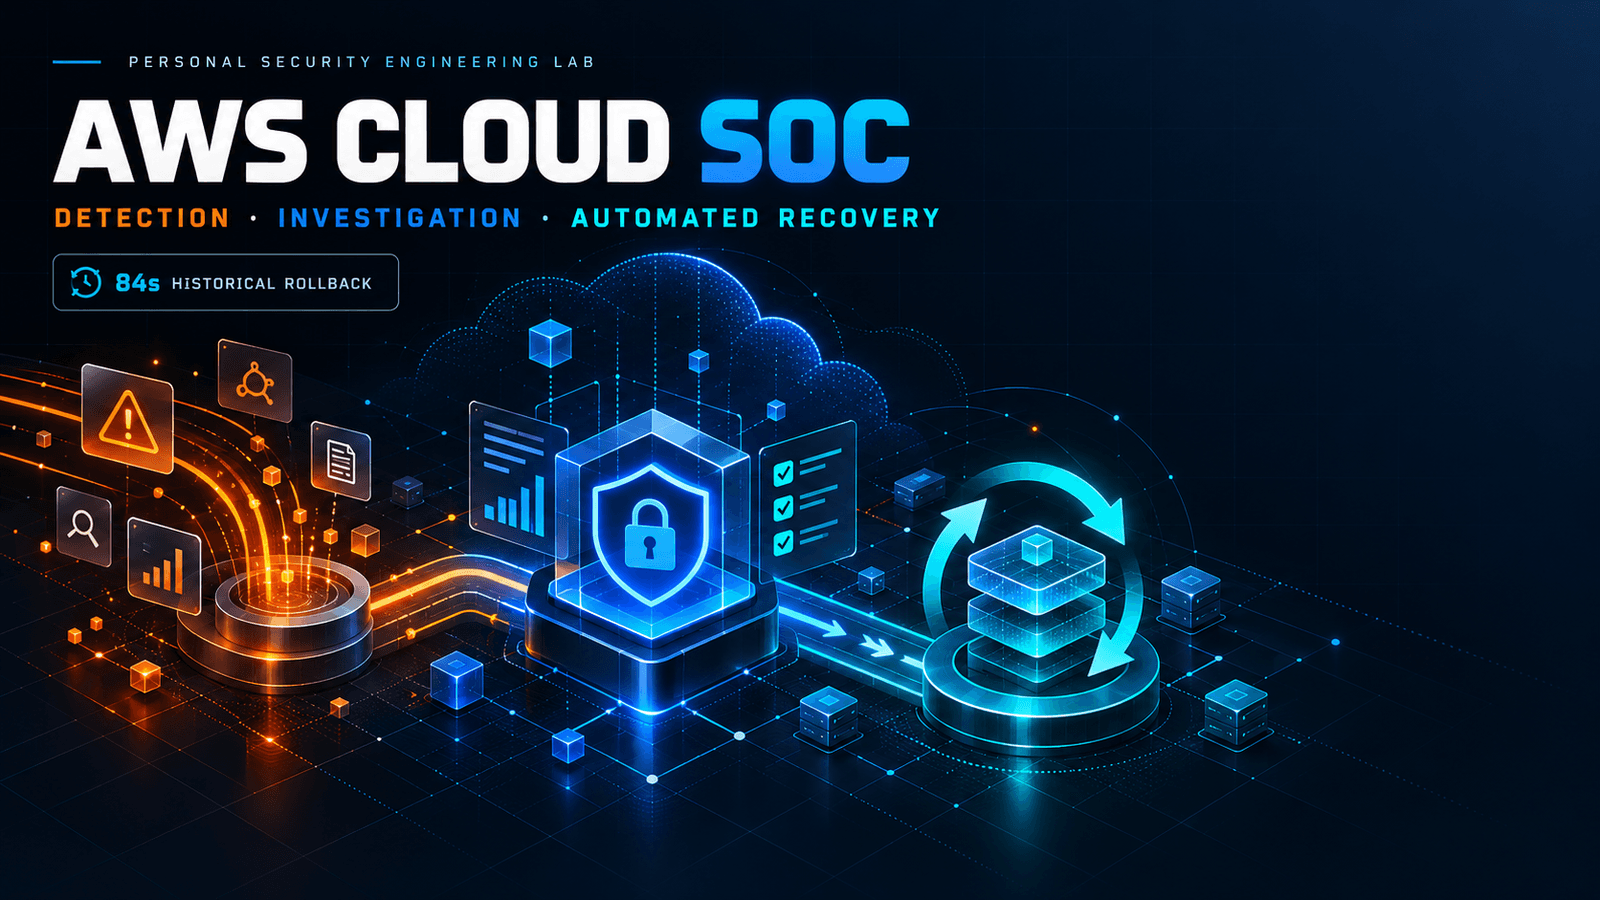
- 60-second configured rollback schedule; 84-second observed automatic recovery of the original security group in a controlled personal AWS lab drill on October 13, 2026.
- Core stack: Python/Boto3, AWS CloudTrail, GuardDuty, EventBridge, Lambda, DynamoDB, SNS, SQS, IAM/SSO, EC2/VPC, CloudWatch, Terraform, Next.js 16/TypeScript and GitHub Actions.
The Problem
Architecture: Two Detection Paths
Approved system architecture — two separate inputs, one gated response path


Read-Only SOC Analyst Cockpit
- Overview: detection metrics, trends, triage breakdown, queue and pipeline.
- Investigations: search, severity/source/disposition filtering and case inspection.
- Case dossier: redacted evidence context, analyst rationale and lifecycle.
- Approval Gate: human-review architecture, cryptographic challenge and separate reviewer permissions.
- Response Operations: scoped canary perimeter and mixed simulated/historical response fixtures.
- Forensic Audit: logical append-only model, activity records and completeness warnings.
- Architecture: trust boundaries and responsibility separation.
- Settings & Posture: local read-only behavior and configuration views.
Synthetic offline dashboard gallery


Human Authorization Before Response
Canary-Only Execution and Recovery-First Ordering
Historical October 13, 2026 Acceptance

Security, Evidence and Limitations

Educational Guide — Download or Read Online
- Download the AWS Cloud SOC educational guide (PDF, 10 pages)
- Read the responsive AWS Cloud SOC educational guide (HTML)
Engineering Takeaways
- Preserve recovery capability before applying containment.
- Distinguish analyst triage from authority to act.
- Make synthetic tests, actual AWS readbacks and historical evidence easy to tell apart.
- Record failed and manual restorations accurately rather than rewriting them as success.
- Keep the portfolio UI read-only and minimize the exposure of private infrastructure details.